
 Cybercrime Patterns Targeting Cloud Infrastructure in 2025
In March 2025, a mid-market SaaS company we monitor watched their AWS bill jump from $14,000 to $310,000 in eleven days. No new product launch. No traffic spike. An at…
 Encryption Key Management Across AWS, Azure, and GCP
It is 3:14 AM and an alert fires from our SIEM. A developer at a fintech client just exported a customer master key reference from a CI pipeline log. The key itself ne…
 SQL Injection in 2026: Why It Still Owns Your Database
In late 2023, the MOVEit Transfer breach hit roughly 2,600 organizations and exposed records belonging to over 90 million people. The root cause? A SQL injection vulne…
 Automated Vulnerability Scanning for Cloud Resources: A Checklist
In March, a fintech client called us at 2 AM because an attacker had pulled 14GB of customer records from an S3 bucket that nobody on their team remembered creating. T…
 Multipartite Virus: Hunting Multi-Vector Malware in Production
A manufacturing client called us on a Tuesday morning with a problem that didn’t add up. Their endpoint agent had flagged and quarantined a suspicious executable on th…
 MITRE ATT&CK Mapping in Sentinel Detection Rules
It is 2 AM and your SIEM fires 47 alerts in three minutes. Forty-five are false positives. The other two are an active intrusion — one flagging suspicious PowerShell e…
 MITRE ATT&CK Integration in Tabletop Exercises: A Checklist
Last quarter, we facilitated a tabletop exercise for a financial services client. Their CISO was confident the IR team could handle a ransomware scenario. Forty-five m…
 Internal vs External IP Analysis in Threat Hunting
Your SIEM fires a high-severity alert at 3 AM. A workstation on the finance VLAN just made an outbound connection to an IP address flagged in three threat intelligence…
 Data-at-Rest Encryption for Cloud Storage: Pick a Strategy
A financial services client we onboarded last year had every firewall rule tuned, MFA enforced across the board, and a clean vulnerability scan. Their cloud storage bu…
 Azure Security Center: A Checklist for Unified Security
During an incident response engagement last month, we traced a lateral movement chain (MITRE ATT&CK T1021.001) across a client’s hybrid environment—Azure VMs, on-prem…
 Windows USB Forensics: Tracking External Device Connections
A financial services client called us on a Friday afternoon. Their DLP solution flagged 14 GB of data copied to a removable device, but the employee had already left t…
 Kubernetes Secrets Management: Encryption at Rest Audit
Last year we were brought in to assess a mid-sized fintech company’s Kubernetes environment after a failed compliance audit. Their security team assumed Kubernetes Sec…
 Ransomware Encryption Analysis: Attack Mechanics on Windows
A managed services client called our SOC at 2:14 AM on a Tuesday. Their file server was throwing access denied errors across three departments. By 2:20 AM we had confi…
 Forensic Triage on Windows: Rapid Evidence Collection
Your SIEM flags a suspicious PowerShell execution on a domain controller at 11:43 PM. The endpoint detection tool confirms process injection consistent with MITRE ATT&…
 Docker Container Security: 15-Checkpoint Audit
It is 2:47 AM. Your SIEM fires a privilege escalation alert on a production Linux host. You pull the process tree and find the origin: a Docker container launched six…
 Cloud Security Posture Management: What Your SIEM Misses
We inherited an environment where an S3 bucket had been publicly readable for 14 months. The client ran monthly vulnerability scans. They had a SIEM. They had endpoint…
 DevSecOps Best Practices: A Pipeline Walkthrough
During an incident response engagement last year, we pulled the deployment logs for a mid-sized financial services company and found something that should have stopped…
 Digital Forensics for Incident Response: Field Guide
Three weeks into a ransomware investigation at a mid-size logistics firm, the IR team handed me what they called a “forensic copy” of the infected server. It had been…
 Threat Hunting Techniques: A SOC Readiness Audit
Your SIEM generated zero critical alerts during the four-hour window on Tuesday night. Your first instinct is to call it a quiet shift. But three of the most damaging…
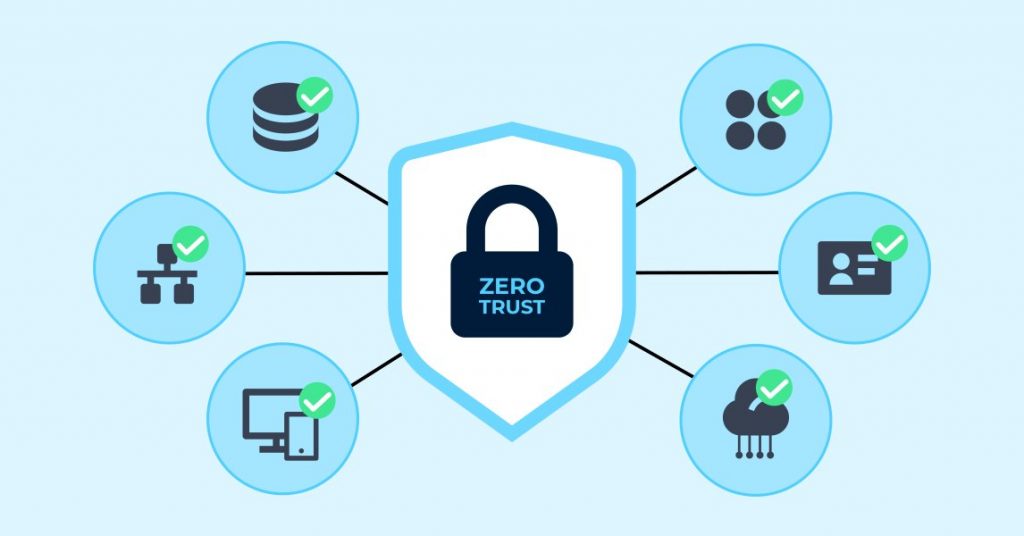 Zero Trust Architecture: A Real Deployment Walkthrough
A financial services firm we work with had a problem they didn’t know they had. Their perimeter firewall was clean. Antivirus showed no alerts. The SOC hadn’t received…
 Cybersecurity Naming Conventions: A Complete IT Guide
Cybersecurity naming conventions are standardized rules for labeling digital assets – including user accounts, firewall rules, log files, and security policies. Organi…
 XaaS Cloud Service Models: Security Guide for IT Teams
Beyond the traditional IaaS, PaaS, and SaaS models, modern cloud computing delivers a growing range of specialized services collectively known as XaaS – Anything as a…
 Challenges in Cloud Computing: Security, Data Management & How to Overcome Them
Related reading: XaaS Cloud Service Models: Security Guide for IT Teams | What Is Veeam Cloud Connect? A Complete Guide for IT Teams | Microsoft Intune Endpoint Manage…
 Endpoint Security: A Complete Guide for IT Teams
Endpoint security is the practice of protecting every device that connects to your organization’s network – laptops, desktops, servers, smartphones, and tablets – from…
 IT Auditing in the Age of AI, IoT, and Zero Trust
IT auditing has never stood still, but the pace of change today is unlike anything the profession has encountered before. From artificial intelligence to interconnecte…
 Windows Digital Forensics Guide for IT Security Teams
When a security incident occurs on a Windows system, the clock starts ticking immediately. Every action taken – or not taken – can determine whether critical evidence…
