
 Cybercrime Patterns Targeting Cloud Infrastructure in 2025
In March 2025, a mid-market SaaS company we monitor watched their AWS bill jump from $14,000 to $310,000 in eleven days. No new product launch. No traffic spike. An at…
 Encryption Key Management Across AWS, Azure, and GCP
It is 3:14 AM and an alert fires from our SIEM. A developer at a fintech client just exported a customer master key reference from a CI pipeline log. The key itself ne…
 SQL Injection in 2026: Why It Still Owns Your Database
In late 2023, the MOVEit Transfer breach hit roughly 2,600 organizations and exposed records belonging to over 90 million people. The root cause? A SQL injection vulne…
 Creating Enforced Authentication Policies in Active Directory
It was 03:14 when the SOC at one of our financial services clients flagged a Tier 0 admin credential authenticating from a workstation in the call center VLAN. The acc…
 Automated Vulnerability Scanning for Cloud Resources: A Checklist
In March, a fintech client called us at 2 AM because an attacker had pulled 14GB of customer records from an S3 bucket that nobody on their team remembered creating. T…
 Intune Compliance Policies: Enforcing Standards Post-Deployment
It is 9 AM on a Monday and the client’s CISO is on the bridge. Their Defender dashboard shows 1,847 enrolled Windows endpoints. Intune says 1,844 are compliant. Their…
 Multipartite Virus: Hunting Multi-Vector Malware in Production
A manufacturing client called us on a Tuesday morning with a problem that didn’t add up. Their endpoint agent had flagged and quarantined a suspicious executable on th…
 MITRE ATT&CK Mapping in Sentinel Detection Rules
It is 2 AM and your SIEM fires 47 alerts in three minutes. Forty-five are false positives. The other two are an active intrusion — one flagging suspicious PowerShell e…
 MITRE ATT&CK Integration in Tabletop Exercises: A Checklist
Last quarter, we facilitated a tabletop exercise for a financial services client. Their CISO was confident the IR team could handle a ransomware scenario. Forty-five m…
 Internal vs External IP Analysis in Threat Hunting
Your SIEM fires a high-severity alert at 3 AM. A workstation on the finance VLAN just made an outbound connection to an IP address flagged in three threat intelligence…
 Azure Security Center: A Checklist for Unified Security
During an incident response engagement last month, we traced a lateral movement chain (MITRE ATT&CK T1021.001) across a client’s hybrid environment—Azure VMs, on-prem…
 PowerShell JEA: Restricting Remote Admin Access
It was 11 PM on a Tuesday when the SIEM flagged a credential harvesting alert on a domain controller. Someone had launched Mimikatz from a PowerShell remoting session…
 Configuring AD Audit Policies with PowerShell and GPO
Last year, a mid-size logistics company we manage came to us after discovering that a domain admin account had been compromised for over three weeks. The attacker used…
 Windows USB Forensics: Tracking External Device Connections
A financial services client called us on a Friday afternoon. Their DLP solution flagged 14 GB of data copied to a removable device, but the employee had already left t…
 Kubernetes Secrets Management: Encryption at Rest Audit
Last year we were brought in to assess a mid-sized fintech company’s Kubernetes environment after a failed compliance audit. Their security team assumed Kubernetes Sec…
 Ransomware Encryption Analysis: Attack Mechanics on Windows
A managed services client called our SOC at 2:14 AM on a Tuesday. Their file server was throwing access denied errors across three departments. By 2:20 AM we had confi…
 Using Autoruns to Audit Every Windows Autostart Location
During a quarterly security review for a client running a 200-seat Windows environment, we found a DLL registered under HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersi…
 Encoding Passwords Securely in PowerShell Enterprise Scripts
Last year we inherited a managed environment from another vendor—a mid-size logistics company running 40+ scheduled PowerShell scripts across their domain controllers…
 Forensic Triage on Windows: Rapid Evidence Collection
Your SIEM flags a suspicious PowerShell execution on a domain controller at 11:43 PM. The endpoint detection tool confirms process injection consistent with MITRE ATT&…
 PowerShell NetIPsec Module: IPsec Policies on Server 2025
We were brought in after a healthcare provider’s internal audit flagged something alarming: a credential-harvesting tool had been sitting quietly on a domain controlle…
 Using the PowerShell Certificate Provider for Cert Management
It is 3 AM. Your SIEM is generating Kerberos pre-authentication failures across 47 workstations. You escalate to Tier 3 and begin triage. The answer is not malware, no…
 IPsec Main Mode Crypto Sets: PowerShell Hardening Guide
A financial services client we took on last year had been running IPsec between their domain controllers and application servers for three years. Solid concept. The ex…
 Set-NetIPsecMainModeCryptoSet: Enforce IKE Encryption in PowerShell
During a network security review for a logistics company we took over last year, we pulled their Windows Server 2025 IPsec policy and found the main mode crypto set ne…
 Docker Container Security: 15-Checkpoint Audit
It is 2:47 AM. Your SIEM fires a privilege escalation alert on a production Linux host. You pull the process tree and find the origin: a Docker container launched six…
 Backup Encryption and Ransomware: A Post-Mortem
The alert came in at 2:47 AM. File shares encrypted. Domain controllers unreachable. The backup server — also encrypted. The client’s IT lead called it a total loss. T…
 Cloud Security Posture Management: What Your SIEM Misses
We inherited an environment where an S3 bucket had been publicly readable for 14 months. The client ran monthly vulnerability scans. They had a SIEM. They had endpoint…
 DevSecOps Best Practices: A Pipeline Walkthrough
During an incident response engagement last year, we pulled the deployment logs for a mid-sized financial services company and found something that should have stopped…
 Digital Forensics for Incident Response: Field Guide
Three weeks into a ransomware investigation at a mid-size logistics firm, the IR team handed me what they called a “forensic copy” of the infected server. It had been…
 Microsoft Defender for Office 365: Configuration Audit Checklist
A financial services client came to us after a compliance review flagged an eleven-day gap in their Office 365 threat detection. They had Microsoft Defender for Office…
 Threat Hunting Techniques: A SOC Readiness Audit
Your SIEM generated zero critical alerts during the four-hour window on Tuesday night. Your first instinct is to call it a quiet shift. But three of the most damaging…
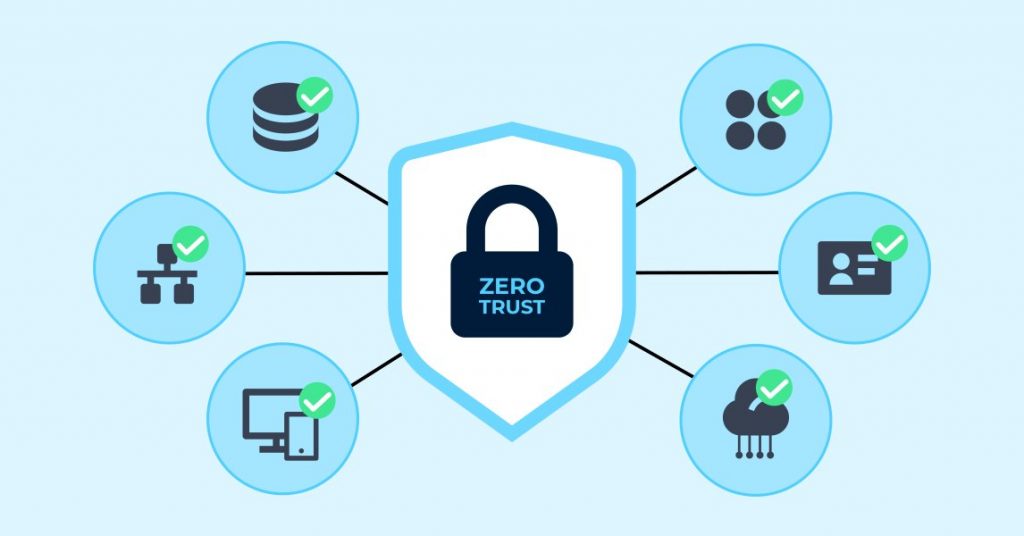 Zero Trust Architecture: A Real Deployment Walkthrough
A financial services firm we work with had a problem they didn’t know they had. Their perimeter firewall was clean. Antivirus showed no alerts. The SOC hadn’t received…
 Active Directory Security: Harden Your AD Environment
In March 2023, Cl0p operators compromised a regional financial services company and reached their domain controllers in 87 minutes. The initial vector was a spearphish…
 Cybersecurity Naming Conventions: A Complete IT Guide
Cybersecurity naming conventions are standardized rules for labeling digital assets – including user accounts, firewall rules, log files, and security policies. Organi…
 XaaS Cloud Service Models: Security Guide for IT Teams
Beyond the traditional IaaS, PaaS, and SaaS models, modern cloud computing delivers a growing range of specialized services collectively known as XaaS – Anything as a…
 Endpoint Security: A Complete Guide for IT Teams
Endpoint security is the practice of protecting every device that connects to your organization’s network – laptops, desktops, servers, smartphones, and tablets – from…
 Windows Digital Forensics Guide for IT Security Teams
When a security incident occurs on a Windows system, the clock starts ticking immediately. Every action taken – or not taken – can determine whether critical evidence…
